

 Newsletters
 Risk Central
 Digital Edition
Sponsored: Liberty Mutual Insurance
How Organizations Can Build Cyber Resilience in an Era of AI-Driven Threats
Cyber risk has fundamentally changed. What was once viewed as a technical concern managed by the IT department has become a core business risk with the potential to disrupt operations, damage revenue, and create legal, regulatory, and reputational fallout. Attackers are moving faster than ever, leveraging automation and artificial intelligence to launch personalized attacks at unprecedented scale.”
For organizations of every size, the question is no longer whether a cyber incident will occur, but how prepared they will be when it does. Building resilience requires a coordinated approach that spans culture, preparation, and the right insurance partnership.
“The biggest shift is that cyber has moved from a technical problem to really a core business risk,” said Erin Halchak, Chief Underwriting Officer, US Cyber, Global Risk Solutions North America, Liberty Mutual Insurance.
“Ransomware still remains a major concern, but the threat has really broadened to include phishing, social engineering, business email compromise, supply chain attacks, and data theft.
The Threats Most Often Overlooked
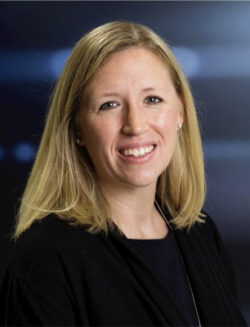
Erin Halchak, Chief Underwriting Officer, US Cyber, Global Risk Solutions North America, Liberty Mutual Insurance
While ransomware continues to dominate headlines, Halchak said two areas of exposure are consistently underestimated by business leaders: the human element and third-party vendor risk.
“Leaders tend to focus on the ransomware headlines that we see, but social engineering and business email compromise quietly drive a very large share of losses,” she said.
“Most organizations don’t fully appreciate how dependent they are on vendors, cloud providers, and other partners. An incident at a third-party can really be just as disruptive as one inside of your walls.”
Effectively managing that vendor exposure means treating it as an extension of the organization’s own risk. Halchak recommends a formal third-party vendor management program that documents contractual relationships and assesses how a breach at a partner could ripple back into the organization’s operations.
Cyber risk can also no longer live solely within the IT department. It must be part of the enterprise conversation, all the way up to the board level.
“A cyber event can interrupt your operations. It affects your revenue. It creates legal liability, regulatory liability, and reputational consequences. Those are business outcomes,” Halchak said. “The responsibility for managing cyber risk really has to go beyond the IT department. It needs to be a part of the organization’s culture from the top all the way down.”
Building a Culture of Preparedness
If leadership sets the tone, employees are the front line. Halchak described staff as a vulnerability and one of the most important defenses an organization has.
“Technology alone cannot eliminate the human element,” she said. “People are often the first encounter to a threat. When we know how to recognize and report suspicious activity — and that there’s a safe way to do that within your organization without the fear of blame — that can be one of your strongest controls.”
The most effective awareness programs, she said, have evolved beyond the once-a-year compliance checkbox. They are frequent, practical, and reflect the actual threats employees face. Just as important, they empower rather than punish.
“You want to build a culture where you’re judged on your reporting rate, and that’s a positive. It’s about communicating, not just running and hiding when something beeps at them.”
Beyond training, organizations should invest in the operational foundations of resilience. Halchak recommends that companies:
- Maintain and regularly update an incident response plan
- Identify key decision-makers and escalation paths in advance
- Understand dependencies on vendors and cloud providers
- Keep current contact information for response partners
- Run tabletop exercises to stress-test the plan
Tabletop exercises — simulations of a breach involving the decision-makers who would be called on in a real event — are among the most valuable tools available.
“A tabletop exercise is a plan on a piece of paper. How do you turn that into a practical response?” Halchak posed.
“Going through the practical response and the exercise really reveals gaps. It provides clarity on who the decision-makers are under pressure, and it builds the muscle memory of a team so that, when it matters, they know how to react.”
She recalled one risk manager who sprung a surprise tabletop on his team at 5:00 p.m. on a Friday. Most of the team believed they were in a real breach.
The exercise exposed weaknesses in the escalation process and how the team would contact breach response vendors when systems were down. Three months later, when a genuine incident struck, that same team responded quickly and significantly reduced the impact of the claim.
“Running through realistic scenarios before an event means far fewer surprises during an event,” Halchak said.
The Evolving Role of the Cyber Insurance Partner
The cyber insurance product has matured significantly over the past decade and so have the buyers purchasing it. What was once seen as merely a policy has evolved into a partnership that can deliver value before, during, and after an incident.
“The underwriting process really encourages productive conversations about controls and preparedness,” Halchak said.
“And then during and after an incident, it gives organizations fast access to expertise and resources when they need them most.”
Coverage, she said, should always be evaluated in the context of an organization’s operations, risk tolerance, and third-party dependencies. But the relationship goes well beyond the policy itself.
“The cyber insurance market has evolved into a partner in risk with their insureds rather than just a policy,” Halchak said.
“The cyber industry matured, and our cyber buyers have matured.”
That partnership approach is especially valuable given the pace at which threats are evolving. Carriers with deep claims experience and visibility across industries can share emerging trends with insureds and help them adapt in real time.
“Last year, we talked so much about third-party supply chain risk. That is something that insureds became incredibly aware of,” Halchak said.
“The trend right now is the speed of these silent ransomware attacks coming from AI and what insureds can do now to protect themselves from that. It’s just this constant evolution.”
Ultimately, Halchak said, the insurer’s role is to help organizations detect, respond, recover, and adapt. That means building resilience as an ongoing discipline rather than a one-time fix.
“The industry helps by pairing capital with expertise,” she said.
“We’re pointing out deficiencies in controls, and then they’re remediating those deficiencies. Hopefully, we’re getting to that before these incidents actually happen. It all goes back to the culture of your enterprise and having that awareness from the top all the way down to the bottom.”
To learn more, visit https://business.libertymutual.com/commercial-insurance-solutions/cyber-insurance/.

This article was produced by the R&I Brand Studio, a unit of the advertising department of Risk & Insurance, in collaboration with Liberty Mutual Insurance. The editorial staff of Risk & Insurance had no role in its preparation.